Tahseen · تحصين · Offline patching
Keep isolated networks patched, without connecting them to the internet.
Tahseen (تحصين, “fortification”) brings OS patches, antivirus signatures and third-party updates into air-gapped networks through a one-way, verified path. Every package is signature-checked and scanned, approved by a second person, and rolled out in phases inside your maintenance windows. Compliance against patch deadlines is visible per site, network and device.
- One-way import with signature checks
- Phased rollout with rollback
- Patch SLAs per network and site
Tahseen · Compliance
Air-gappedManaged devices
12,480
Compliant
94%
Past critical SLA
312
- Monthly cumulative updateRing 2 · 1,872 devices · 98% successAdvancing
- Antivirus signaturesAll workstations · 9,240 devicesDeploying
- Browser security updateWaiting for a second approverApproval
- e-Gate firmwareSpecialised devices · 2 failedRollback
Authorized vendor to
- Ministry of Finance
- Ministry of Interior
- DGE Abu Dhabi
- Etihad Aviation
- EDGE Group
Delivered for
- Hindustan Unilever
- Nokia
- Linde
- USA Today
- JSL
Procurement-ready
- Abu Dhabi Government Procurement Gate
- UAE Ministry of Finance, federal procurement
- Registered ADNOC vendor
- National ICV certificate
Product tour
See Tahseen at work
Screens from Tahseen, shown with sample data for an air-gapped network.
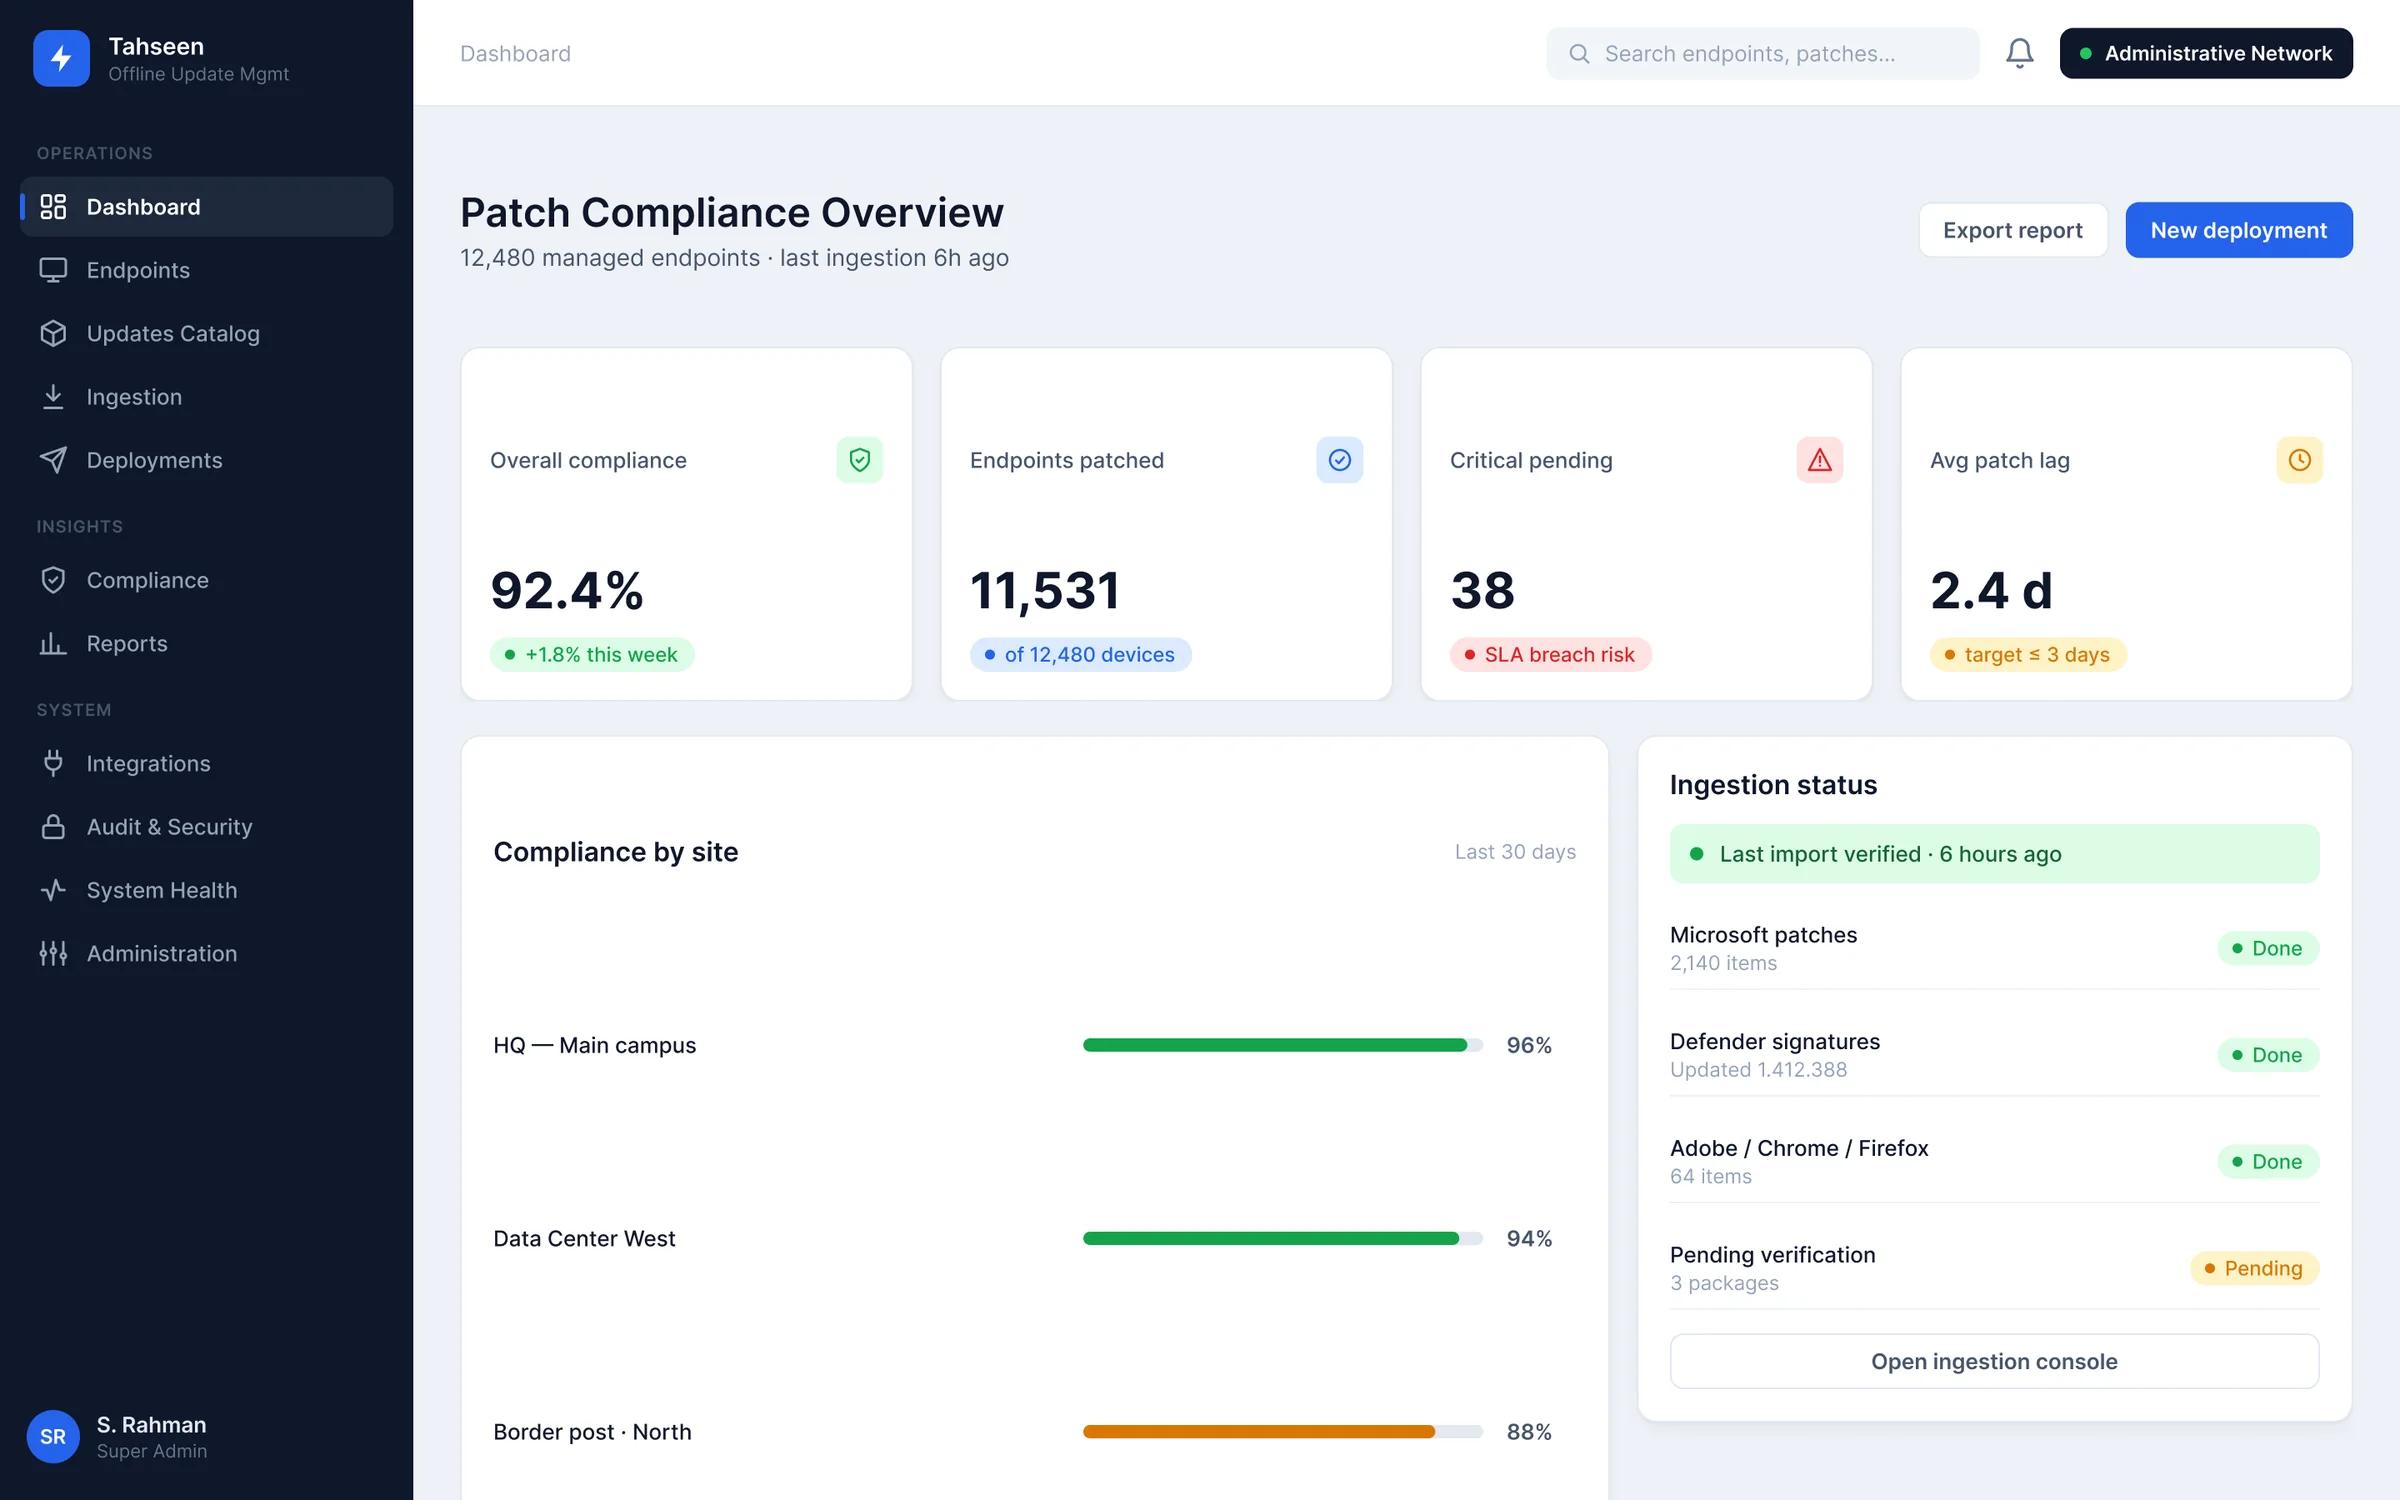
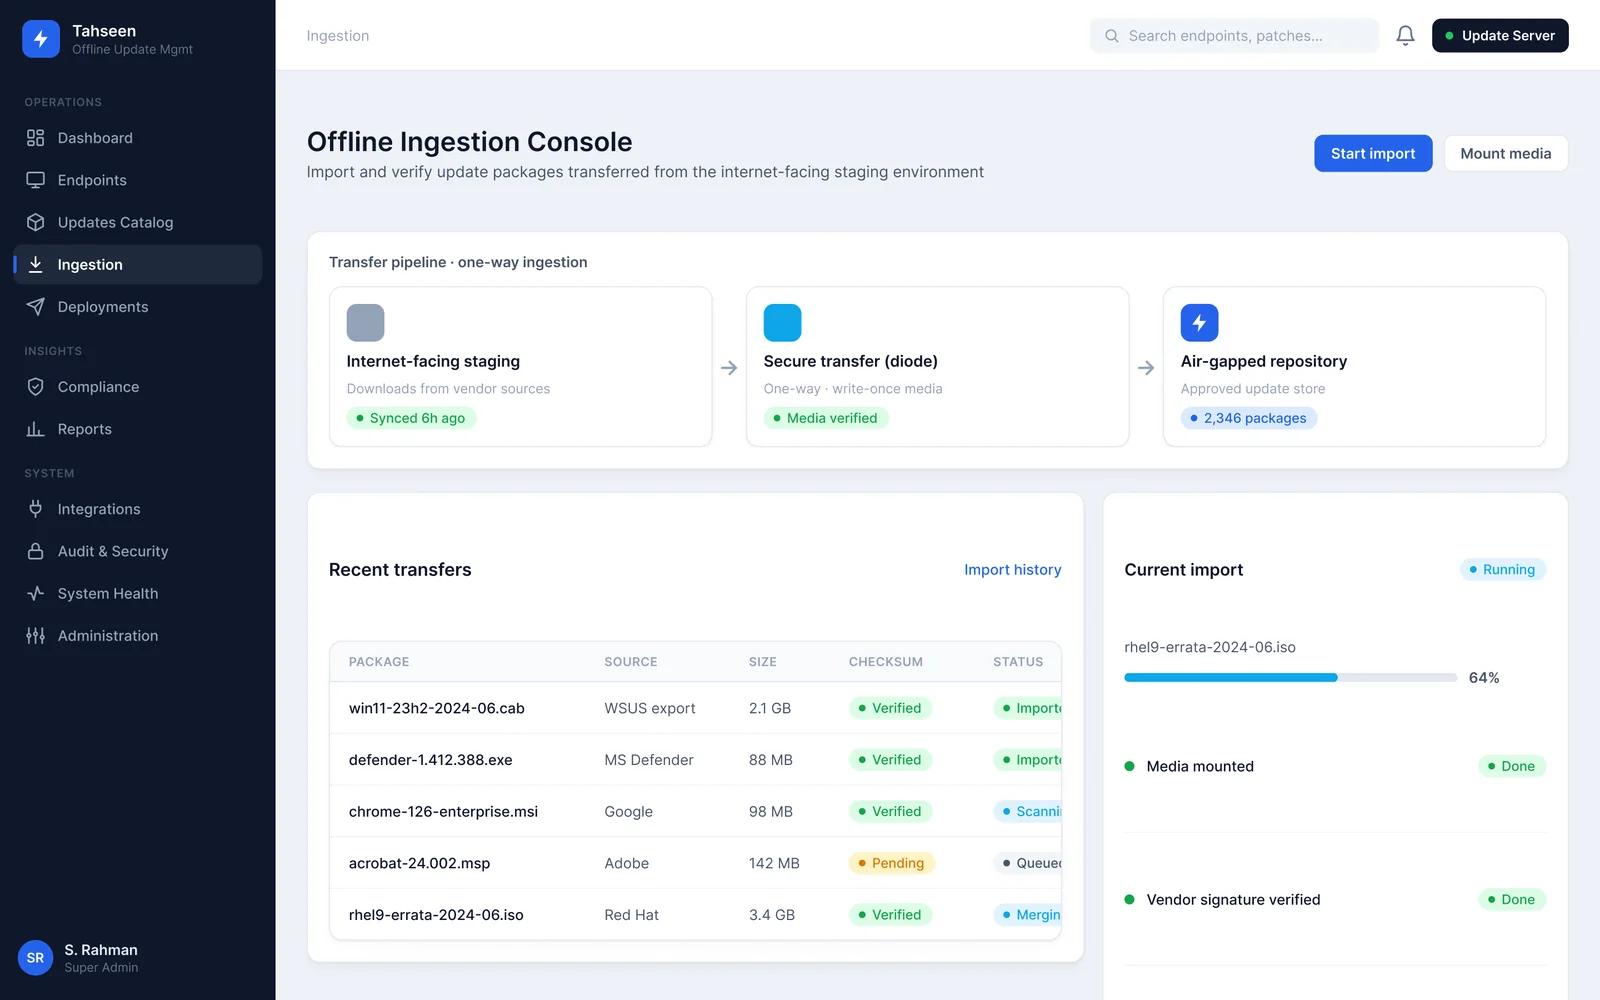
Patching without internet
Updates for Windows, Linux and common applications reach air-gapped networks through a controlled one-way import.
Every package verified
Checksums and vendor signatures are checked before anything reaches an endpoint.
Compliance you can show
Compliance by site and SLA reports for auditors, from the same data.
Why it matters
Isolated doesn’t mean protected
Air-gapped networks keep attackers out, but they also keep updates out. Patching them by hand leaves gaps that last for months.
Months behind on critical patches
Updates are carried in on USB drives when someone has time, so known vulnerabilities stay open.
No proof of what was installed
Spreadsheets cannot show auditors which devices were patched, when and by whom.
Unverified media
Packages brought across the gap without signature checks or scanning are a risk in themselves.
What Tahseen does
From the vendor’s release to a compliant device
Offline ingestion
Packages downloaded in an internet-facing staging area cross on one-way, write-once media, then are signature-checked and malware-scanned.
Updates catalogue
OS patches, antivirus signatures and third-party updates, with the vulnerabilities each one fixes, supersedence and prerequisites.
Approvals
Updates are reviewed before deployment, and the person who requests an update can never be its only approver.
Endpoints and discovery
Windows and Linux servers and workstations by site and network, with scans that find unmanaged devices to enrol.
Specialised devices
Biometric readers, e-gates, CCTV and forensic systems get their own groups and patch handling.
Phased deployment
Pilot, canary and broad rings that advance only on success, inside maintenance windows, with bandwidth limits for remote sites.
Rollback
Failed devices are listed with the reason, and updates can be rolled back by device, group or ring.
Compliance and SLAs
Patch deadlines by severity, compliance by site, network and OS, and open vulnerabilities mapped to devices.
Self-service for staff
Employees see pending updates on their device, ask to defer a reboot or request approved software.
How it works
Across the air gap, one verified step at a time
- 01
Import
Updates cross on one-way media and are verified against vendor signatures and scanned before they enter the repository.
- 02
Approve
The security team reviews each update, its dependencies and the vulnerabilities it fixes, and approves it.
- 03
Deploy
Updates roll out ring by ring inside maintenance windows, and a ring advances only when success clears your threshold.
- 04
Prove
Dashboards and reports show compliance against your patch deadlines, and every action is in the audit log.
Who it’s for
Built for networks that can never touch the internet
Security and interior agencies
Classified and operational networks spread across headquarters, branches and border sites.
Defence and critical infrastructure
Isolated IT and operational networks in energy, utilities and transport.
Regulated enterprises
Banks and companies with segregated networks that must prove patch compliance to auditors.
Licensing
License Tahseen for your own network
Tahseen is sold as a software licence, not a one-off project. You choose where it runs; the product, updates and support are the same.
On-premise licence
Runs on your servers
Install Tahseen in your data center, in your private cloud tenant or on an isolated network with no internet connection.
- Annual licence, priced by the number of managed devices
- Your data never leaves your network
- Installation, training and updates included
- Support with agreed response times
Hosted evaluation
Try it before you install
A hosted Tahseen environment with sample data, so your team can test it on its own scenarios before installation. Production always runs on your network.
- Sample data only, never your records
- Your scenarios walked through with our specialists
- Moves to your servers when you are ready
The price depends on the number of managed devices and the support level. We reply within one business day and send a written quote after a short scoping call.
Track record
Trusted by UAE government entities and global brands.
Authorized vendor to five UAE government entities, with projects delivered for Hindustan Unilever, USA Today, Nokia and Linde.
- Startups and enterprises served by our engineering teams
- 150+
- Startups and enterprises served by our engineering teams
- Average rating on Clutch, Trustpilot and Glassdoor
- 4.9/5
- Average rating on Clutch, Trustpilot and Glassdoor
- Client satisfaction rate
- 98%
- Client satisfaction rate
- UAE government entities we are an authorized vendor to
- 5
- UAE government entities we are an authorized vendor to
Hear it from our clients
Client testimonial
E-commerceClient testimonial
HealthcareClient testimonial
E-commerceClient testimonial
E-commerce
Security
Designed for classified environments
No internet connection
Tahseen runs entirely inside the isolated network; nothing calls out.
Signed and verified
Your own certificate authority signs agents and updates, and every package is verified before use.
Tamper-evident audit
Every administrative and system action is written to a write-once (WORM) audit store.
Separation of duties
Role-based access, multi-factor authentication and two-person approval for updates and role changes.
Book a demo
See Tahseen patch an isolated network
We walk your team through an offline import, an approval, a phased rollout with a rollback and the compliance report, in English or Arabic.
- A live demo, not slides
- Mapped to your networks and sites
- Under NDA if you need one
4.9/5 average rating · 98% client satisfaction · 150+ clients served
FAQ
Offline patch management questions, answered
What is Tahseen?
Tahseen is patch and update management for air-gapped and isolated networks. It imports OS patches, antivirus signatures and third-party updates through a one-way, verified path, deploys them in phases and reports compliance against your patch deadlines.
How do updates get into the isolated network?
Packages are downloaded in an internet-facing staging area and carried across on one-way, write-once media. Inside the network, Tahseen checks vendor signatures and integrity and scans every package before it can be approved.
What can it patch?
Windows and Linux servers and workstations, antivirus signatures, common third-party applications such as browsers and document readers, and specialised devices such as e-gates, biometric readers and CCTV systems, each with its own handling.
What happens if an update breaks something?
Rollouts move through pilot, canary and broad rings and only advance when success stays above your threshold. Failed devices are listed with the reason, and the update can be rolled back.
Does it work across remote sites?
Yes. Devices are grouped by site and network, deployments to remote sites are throttled to the bandwidth you set, and compliance can be drilled down to a single site.
Does it support Arabic?
Yes. The console works in Arabic and English, right to left, with Hijri and Gregorian dates.
How is Tahseen licensed?
As an annual on-premise licence installed on your own servers or an isolated network, with installation, training, updates and support. A hosted evaluation environment with sample data is available before installation.
Close the patch gap on your isolated networks
Book a live Tahseen demo for your security team.
Book a Tahseen demo