Falaj · فلج · SAST, DAST and SCA
Find vulnerabilities before release, without your code leaving the UAE.
Falaj tests your applications for security flaws at every stage: static analysis of the code, dynamic tests of the running app, open-source dependencies and leaked secrets. Policies decide when a pipeline passes, warns or stops, developers get the fix in their merge request, and the security team sees one risk picture. It runs inside your network or in a UAE sovereign cloud.
- SAST, DAST, SCA and secrets in one platform
- A security gate in every pipeline
- On-premises or UAE sovereign cloud
Falaj · Pipeline gate
Policy · Tier 1SAST
1 new
critical
SCA
214
packages · SBOM signed
Secrets
0
found
- SQL injection · CWE-89APP-07 · OrdersController.cs:142Critical
- Vulnerable package · fix availableAPP-07 · dependency upgradeHigh
- Cookie without Secure flagAPP-07 · DAST · stagingAccepted
Authorized vendor to
- Ministry of Finance
- Ministry of Interior
- DGE Abu Dhabi
- Etihad Aviation
- EDGE Group
Delivered for
- Hindustan Unilever
- Nokia
- Linde
- USA Today
- JSL
Procurement-ready
- Abu Dhabi Government Procurement Gate
- UAE Ministry of Finance, federal procurement
- Registered ADNOC vendor
- National ICV certificate
Product tour
See Falaj at work
Screens from Falaj, shown with sample applications and findings.
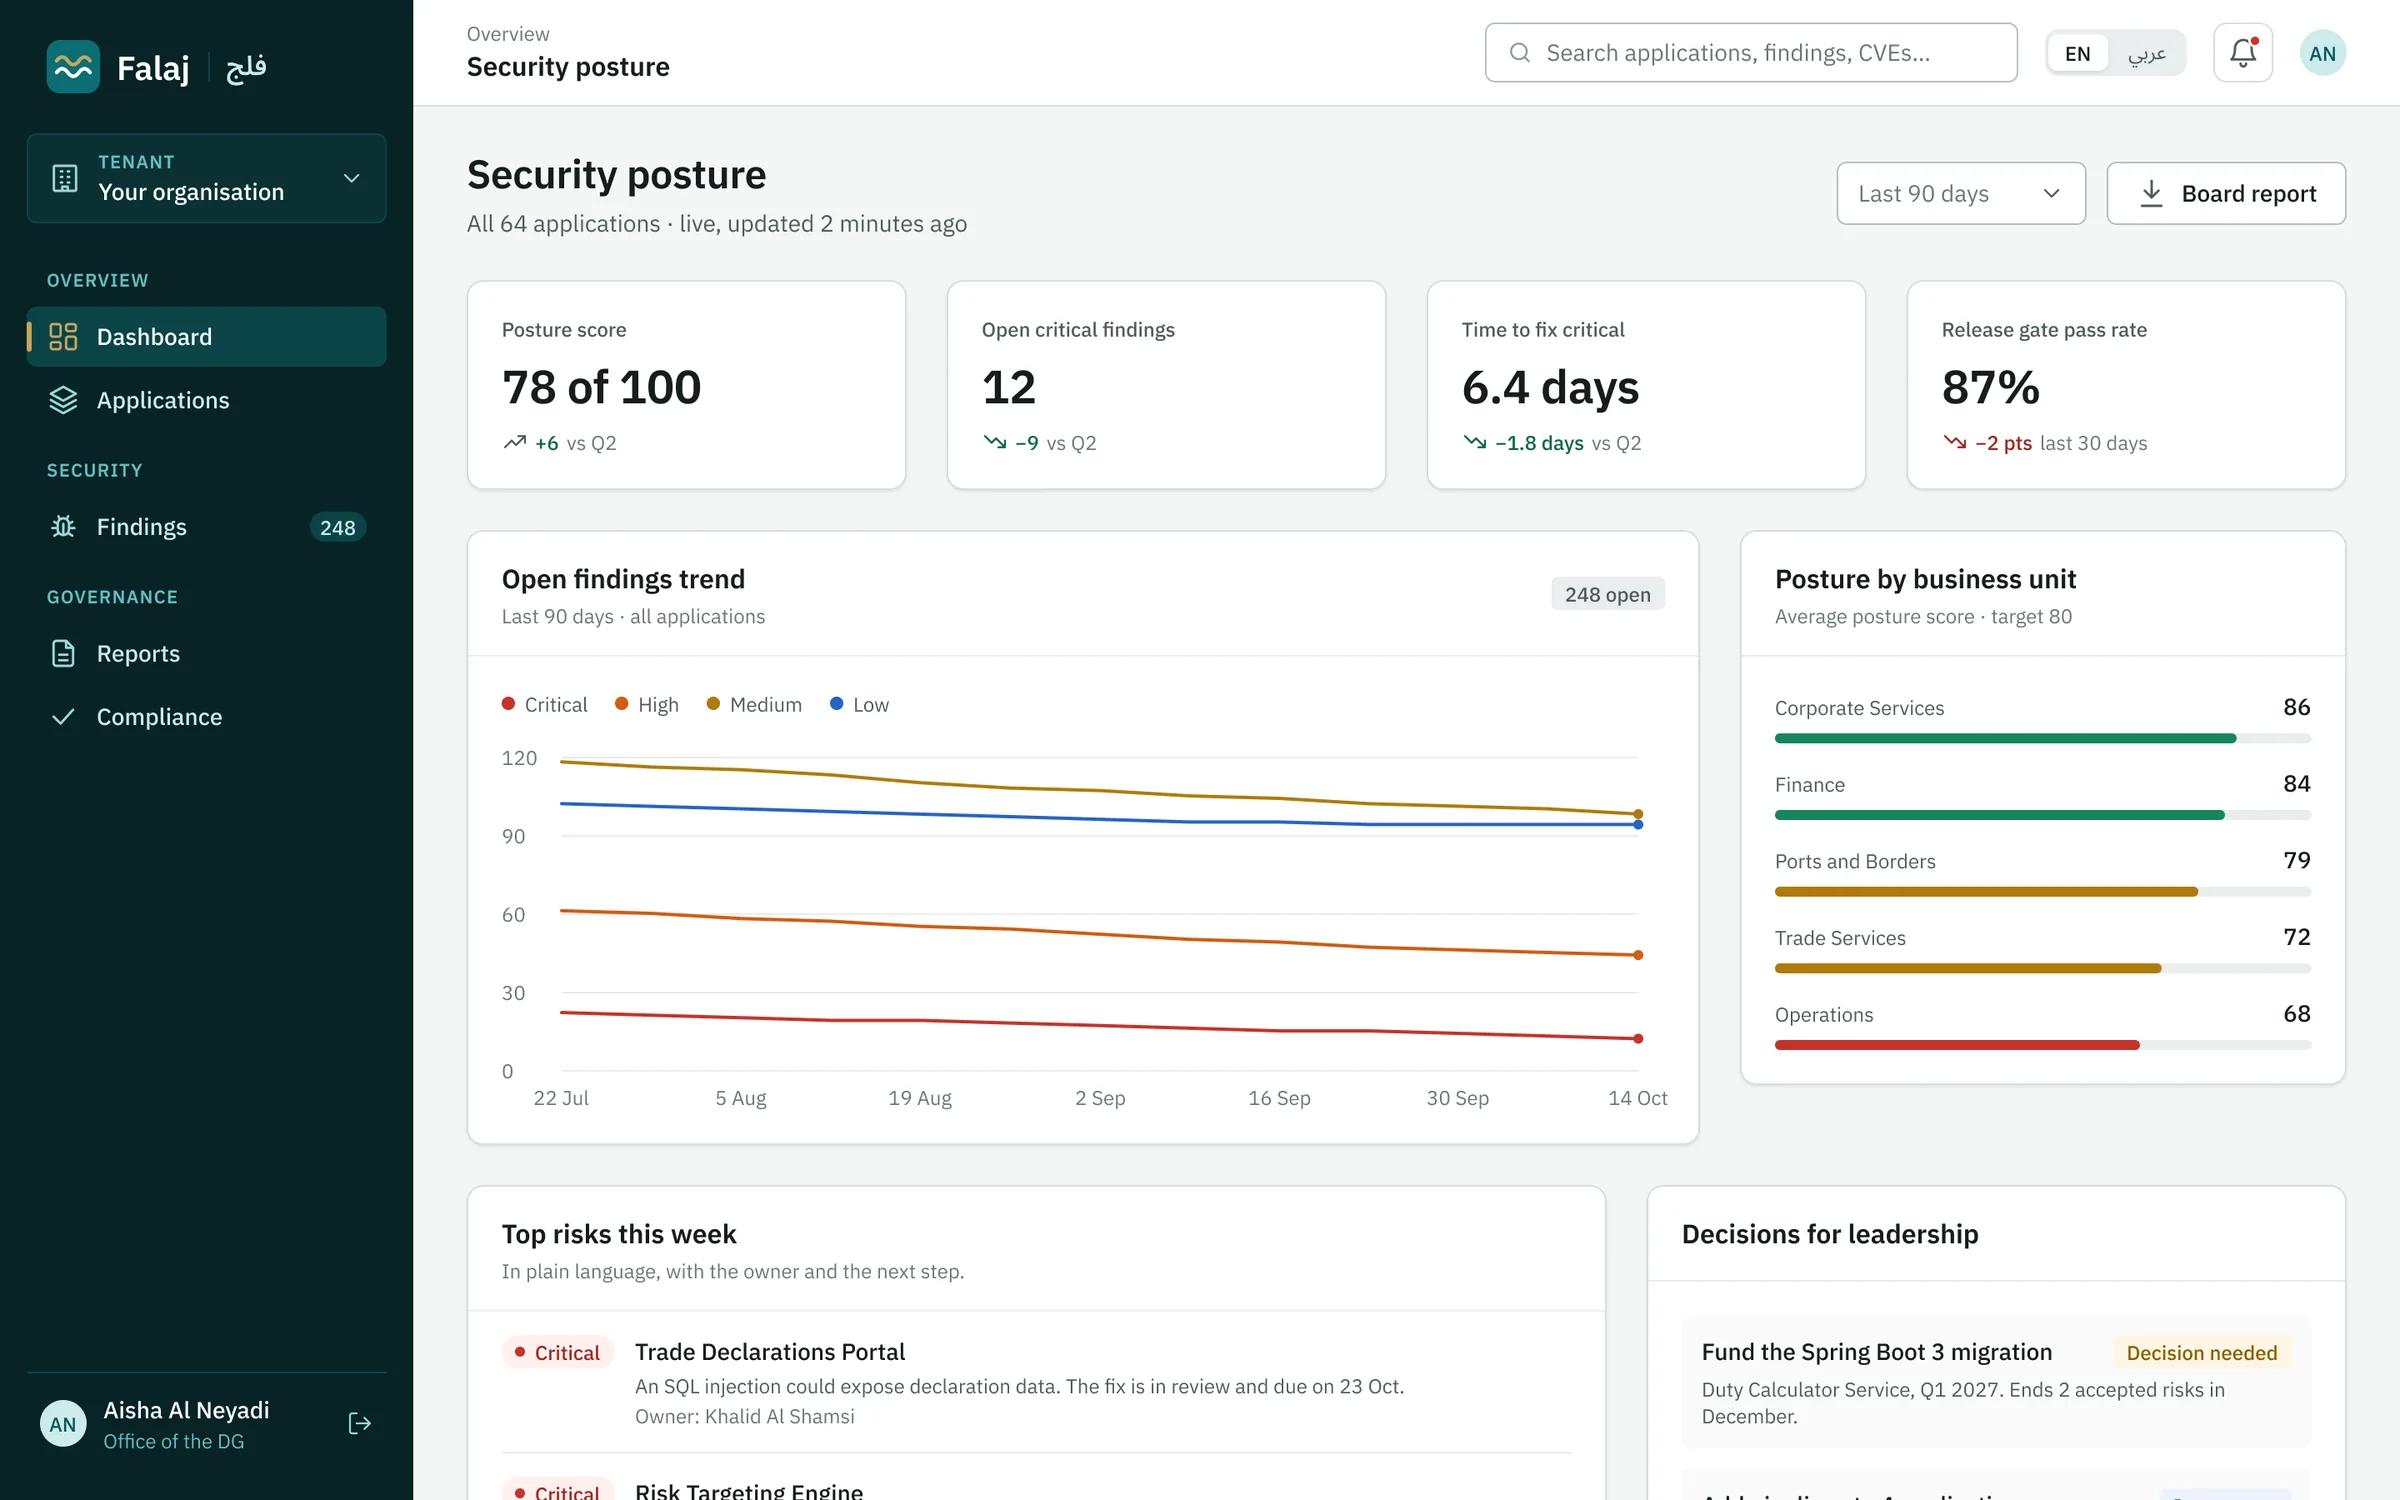
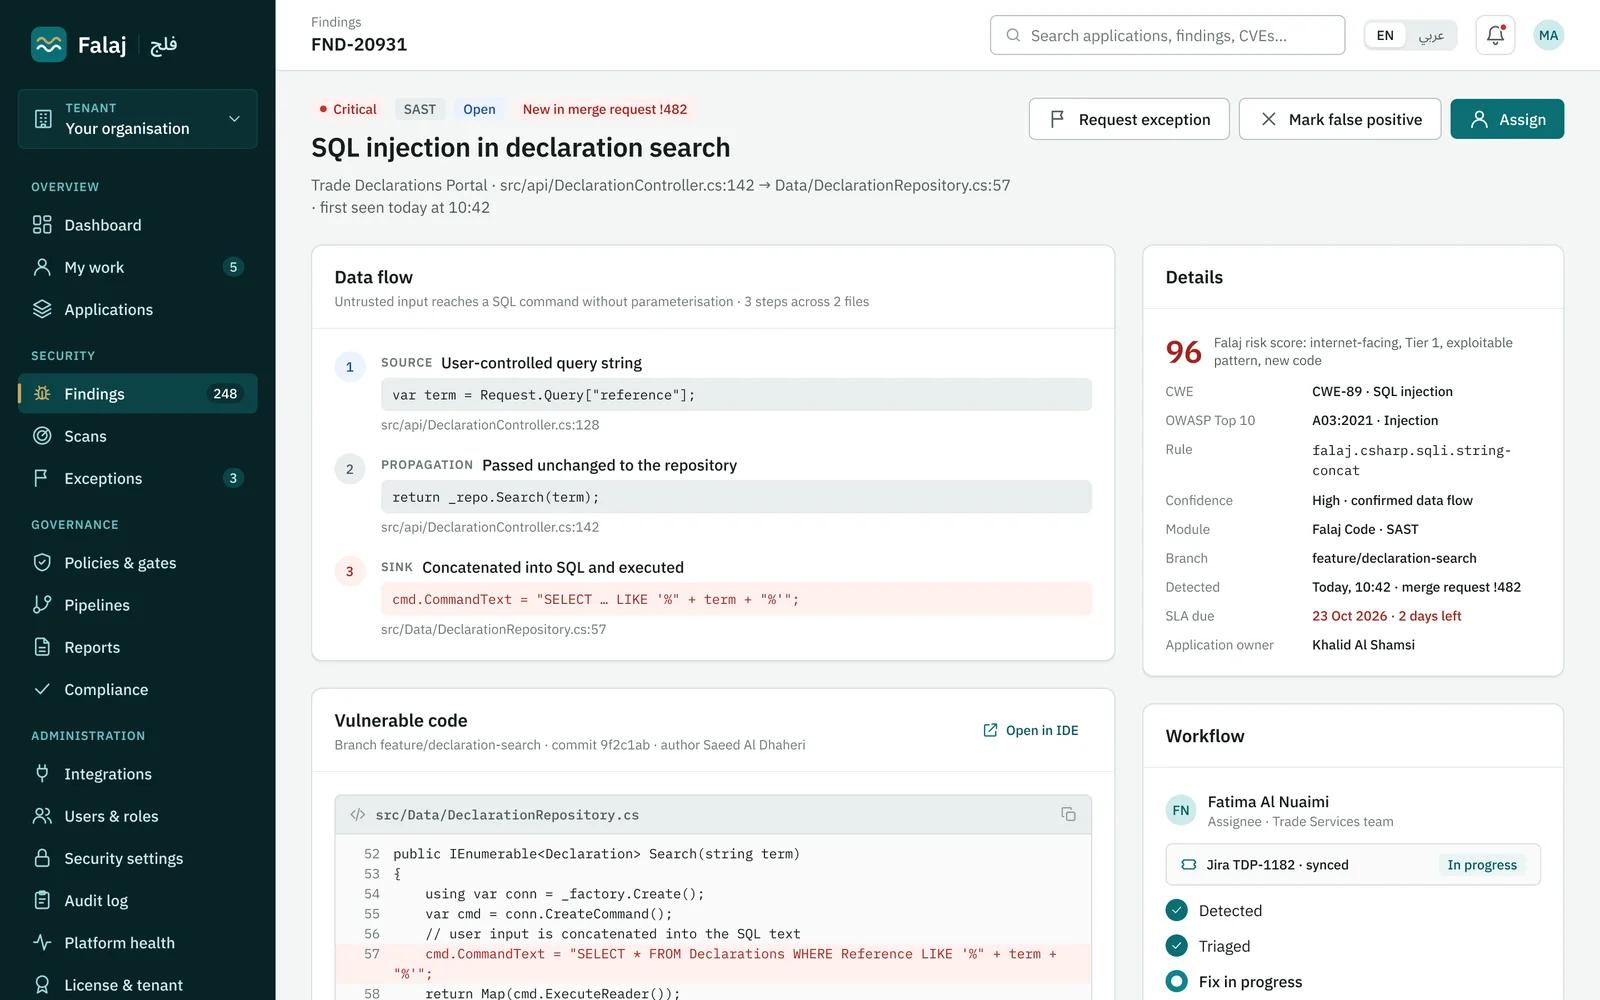
SAST, DAST, SCA and secrets together
One platform for code, running apps, dependencies and leaked secrets, so findings are not scattered.
A gate in every pipeline
Policies decide when a merge request passes, warns or stops, and developers see the fix in the merge request.
Plain language for leaders
Top risks and decisions for leadership are written for people who do not read code.
Why it matters
Security testing that arrives too late, or never
Most organisations test applications once a year, with tools that send code abroad and reports nobody can act on.
Flaws reach production
Penetration tests happen after release, so injection flaws and exposed secrets are found by attackers first.
Code leaves the country
Cloud scanners upload source code and findings to servers outside the UAE, which many entities cannot allow.
Noise instead of fixes
Several scanners produce thousands of duplicate results, and developers stop reading them.
What Falaj does
Every test, one gate, one risk picture
Static analysis (SAST)
Scans source code for flaws such as SQL injection and broken authorisation, and shows the path from input to the vulnerable line.
Dynamic testing (DAST)
Tests running applications in staging, including signed-in journeys, with credentials kept in your vault.
Dependencies and SBOM (SCA)
Finds vulnerable and risky open-source packages, checks their licences and produces a signed CycloneDX SBOM.
Secrets detection
Catches passwords, keys and tokens committed to code before they reach a shared branch.
Policy gates
Policies decide when a pipeline passes, warns or is blocked, by application criticality, business unit or individual app.
Findings that get fixed
Results are de-duplicated and ranked by risk, with fix guidance in the developer’s merge request, IDE and chat.
Exceptions with approval
Risk acceptances need a justification, compensating controls and two approvals, and reopen when they expire.
Reports and evidence
Executive and technical reports, OWASP Top 10 and CWE coverage, SARIF exports and a hash-chained audit log.
Integrations
GitLab, GitHub Enterprise, Azure DevOps Server and Jenkins, Jira and ServiceNow, your SIEM and single sign-on.
How it works
From the first repository to a gate in every pipeline
- 01
Connect
Connect a repository and pipeline with a versioned template; a baseline scan starts straight away.
- 02
Scan
Falaj runs static, dependency and secrets scans on every change, and dynamic tests on staging.
- 03
Gate
The policy for that application decides whether the pipeline passes, warns or stops.
- 04
Fix and prove
Developers fix with the guidance shown, Falaj verifies the fix, and reports show the trend.
Who it’s for
Built for organisations that build software
Government entities
Entities that build or commission digital services and must keep code and findings in the UAE.
Banks and regulated companies
Teams that must show regulators and auditors how every release was tested.
Software teams and vendors
Development teams and suppliers who want security checks inside their own pipelines.
Licensing
License Falaj on your servers or in the cloud
Falaj is sold as a software licence, not a one-off project. You choose where it runs; the product, updates and support are the same.
On-premise licence
Runs on your servers
Install Falaj in your data center, in your private cloud tenant or on an isolated network with no internet connection.
- Annual licence, priced by the number of applications and developers
- Your data never leaves your network
- Installation, training and updates included
- Support with agreed response times
Cloud subscription
Hosted for you
We run Falaj for you in a UAE data center, or in a cloud region in your country, ready in days.
- Monthly or annual subscription, priced by the number of applications and developers
- Hosting, backups and monitoring included
- Updates applied for you
- Single sign-on and role-based access
The price depends on the number of applications and developers and the support level. We reply within one business day and send a written quote after a short scoping call.
Track record
Trusted by UAE government entities and global brands.
Authorized vendor to five UAE government entities, with projects delivered for Hindustan Unilever, USA Today, Nokia and Linde.
- Startups and enterprises served by our engineering teams
- 150+
- Startups and enterprises served by our engineering teams
- Average rating on Clutch, Trustpilot and Glassdoor
- 4.9/5
- Average rating on Clutch, Trustpilot and Glassdoor
- Client satisfaction rate
- 98%
- Client satisfaction rate
- UAE government entities we are an authorized vendor to
- 5
- UAE government entities we are an authorized vendor to
Hear it from our clients
Client testimonial
E-commerceClient testimonial
HealthcareClient testimonial
E-commerceClient testimonial
E-commerce
Security
Your code stays where you put it
Inside your network
Each service runs as a container in your data center, or in a UAE sovereign cloud, or both.
Every byte in the UAE
Code snippets, findings, logs, backups and configuration all stay in the UAE.
Sign-in and roles
Single sign-on with multi-factor authentication, directory sync, roles and a sealed break-glass account.
Tamper-evident audit
Every sign-in, change and decision is hash-chained and streamed to your SIEM.
Book a demo
See Falaj gate a real pipeline
We connect a sample application, run static, dependency and secrets scans, block a release with a policy and walk through the fix, in English or Arabic.
- A live demo, not slides
- Mapped to your pipelines and tools
- Under NDA if you need one
4.9/5 average rating · 98% client satisfaction · 150+ clients served
FAQ
Application security questions, answered
What is Falaj?
Falaj is an application security testing platform. It combines static analysis (SAST), dynamic testing (DAST), dependency and licence checks (SCA) and secrets detection, with policy gates in your pipelines and one view of risk across all your applications.
Does our source code leave the UAE?
No. Falaj runs inside your network or in a UAE sovereign cloud, and code snippets, findings, logs and backups all stay in the UAE.
Which tools does it work with?
GitLab, GitHub Enterprise, Azure DevOps Server and Jenkins pipelines; Jira and ServiceNow for tickets; Microsoft Teams and email for alerts; plug-ins for VS Code, Visual Studio and JetBrains IDEs; and your SIEM for audit events.
Will it block our releases?
Only when your policy says so. Each policy decides when a pipeline passes, warns or is blocked, for example blocking new critical findings on high-criticality applications. Overrides are time-limited and recorded.
How do you handle false positives?
Results from every scanner are de-duplicated and ranked by risk. An analyst can mark a false positive, with a second reviewer, and turn it into a tuning rule so it does not come back.
Can we use it for our suppliers’ code?
Yes. Falaj is multi-tenant, so supplier teams can be onboarded with their own applications, pipelines and policies.
How is Falaj licensed?
As an annual on-premise licence installed on your servers, private cloud or an isolated network, or as a monthly or annual cloud subscription that we host in a UAE data center or a cloud region in your country. Both include updates and support.
Ship secure code, and keep it in the UAE
Book a live Falaj demo for your development teams.
Book a Falaj demo